Radical Technologies
-OTHER
★★★★★
(2,095 ratings)  50,000+ Student

ISO/IEC 27001:2022 LEAD AUDITOR

ISO/IEC 27001:2022 Lead Auditor Training is a 24-hour, practical and job-oriented course designed to develop the skills required to plan, conduct, report, and follow up on Information Security Management System (ISMS) audits. Learners will understand ISO/IEC 27001:2022 requirements, audit planning, risk and control assessment, audit evidence, nonconformity reporting, corrective actions, and audit team leadership. Ideal for information security professionals, auditors, consultants, compliance professionals, IT managers, and professionals involved in ISMS implementation or auditing.

RT
Radical Technologies
50,000+ English 24 hours Weekdays / Weekends Classroom / Online / Corporate
Online / Classroom

ISO/IEC 27001:2022 LEAD AUDITOR

IT Training Programme

Duration 24 hours
Batch Type Weekdays / Weekends
Mode of Training Classroom / Online / Corporate
Locations Pune, Bangalore, Kochi
Language English
Certification Globally Recognized
Call Now

100% placement assistance

Enquire Now

Get course fees, batch dates & a callback

We never share your details.

What you'll learn

Understand core concepts and architecture from the ground up
Get hands-on with the tools used by working professionals
Build real-world projects you can add to your portfolio
Learn industry best practices and coding standards
Practice with real datasets and real-world scenarios
Prepare for certification and technical interviews
Work on collaborative, team-based exercises
Apply performance tuning and optimization techniques
Understand how the technology fits into a larger ecosystem
Complete assignments reviewed by mentors

Programme Overview

22 sections covering the complete curriculum — a single, progressive learning arc.

24 hours
Training Duration
22
Core Modules
545
Total Lessons
4.7★
Average Rating
50K+
Students Trained
01

Foundations & Core Concepts

Get hands-on with the fundamentals and architecture — the building blocks for everything that follows.

Fundamentals Architecture Setup
02

Hands-On Practical Training

Work through real exercises and assignments designed to mirror what you will do on the job.

Practicals Assignments Labs
03

Real-World Projects

Apply what you have learned to end-to-end projects that go straight into your portfolio.

Projects Portfolio Case Studies
04

Advanced Techniques

Go beyond the basics with advanced concepts, integrations and production-grade practices.

Advanced Integration Best Practices
05

Ecosystem Integration

Understand how this technology connects with the broader tools and platforms used in the industry.

Ecosystem Tools Platforms
06

Performance & Interview Prep

Master optimization techniques and prepare for the technical interview questions employers actually ask.

Optimization Interview Prep Certification

Who is this programme for?

Whether you're already writing code, working with data, or supporting applications today — this programme is built to take you into a -OTHER role.

Software Developers

Engineers who want to add this skill set to their toolkit

Analysts & Consultants

Professionals moving into a more technical, hands-on role

IT Professionals

System admins and support engineers upskilling into a new domain

Fresh Graduates

CS/IT graduates aiming for a job-ready technical role

Course Curriculum

22 sections  •  545 lessons  •  24 hours

01 1. Course Overview
This course is designed to develop the knowledge and practical skills required to plan, conduct, report, and follow up first-party, second-party, and third-party audits of an Information Security Management System.
Participants will learn how to evaluate an organization’s ISMS against ISO/IEC 27001:2022 requirements, assess information security risks and controls, identify audit evidence, document nonconformities, prepare audit reports, and lead an audit team.
02 2. Prerequisites

Participants should have:

• Basic knowledge of information security
• Understanding of management-system concepts
• Familiarity with the Plan–Do–Check–Act cycle
• Basic awareness of risk management
• Knowledge of organizational processes and documentation
• Basic understanding of ISO/IEC 27001 requirements is recommended
• Experience in IT, cybersecurity, compliance, quality, risk, or internal auditing is beneficial
03 Module 1: Information Security and ISMS Fundamentals

Topics Covered

• Information security concepts
• Confidentiality, Integrity, and Availability
• Information assets and asset ownership
• Information security threats and vulnerabilities
• Information security risks and impacts
• Information security objectives
• Introduction to Information Security Management Systems
• Benefits of implementing an ISMS
• ISMS lifecycle
• Plan–Do–Check–Act model
• Risk-based thinking
• Management commitment and continual improvement
• Relationship between information security, business continuity, privacy, and compliance

Practical Exercise

• Identify information assets in a sample organization
• Prepare a basic information security risk scenario
• Map business objectives to information security objectives
04 Module 2: ISO/IEC 27001:2022 Standard Requirements

Clause 4: Context of the Organization

• Understanding the organization and its context
• Internal and external issues
• Interested parties and their requirements
• Determining the scope of the ISMS
• Establishing and maintaining the ISMS
• Scope exclusions and their justification
• Understanding business processes and information flows

Clause 5: Leadership

• Leadership and commitment
• Information security policy
• Roles, responsibilities, and authorities
• Top management responsibilities
• Information security governance
• Management accountability

Clause 6: Planning

• Actions to address risks and opportunities
• Information security risk assessment
• Information security risk treatment
• Risk acceptance criteria
• Risk owners
• Information security objectives
• Planning changes to the ISMS

Clause 7: Support

• Resources
• Competence
• Awareness
• Communication
• Documented information
• Document creation and updating
• Document control
• Evidence of competence and awareness

Clause 8: Operation

• Operational planning and control
• Information security risk assessment execution
• Information security risk treatment implementation
• Change management
• Outsourced processes
• Operational evidence

Clause 9: Performance Evaluation

• Monitoring and measurement
• Analysis and evaluation
• Internal audit
• Audit-program management
• Management review
• Management review inputs and outputs
• Performance indicators and audit evidence

Clause 10: Improvement

• Continual improvement
• Nonconformity
• Corrective action
• Root-cause analysis
• Effectiveness verification
• Improvement records

Practical Exercise

• Interpret ISO/IEC 27001 clauses using sample organizational evidence
• Identify conformity and nonconformity
• Prepare a clause-to-evidence mapping document
05 Module 3: Annex A Information Security Controls

Overview of Annex A

• Purpose of Annex A
• Relationship between risk assessment and control selection
• Statement of Applicability
• Control applicability and justification
• Control ownership
• Control implementation evidence
• Control monitoring and review

Organizational Controls

• Policies for information security
• Information security roles and responsibilities
• Segregation of duties
• Management responsibilities
• Contact with authorities and interest groups
• Threat intelligence
• Information security in project management
• Inventory of information and associated assets
• Acceptable use of information assets
• Return of assets
• Classification and labelling of information
• Information transfer
• Access control
• Supplier relationships
• Cloud-service security
• Incident management
• Business continuity
• Legal, statutory, regulatory, and contractual requirements

People Controls

• Screening
• Terms and conditions of employment
• Security awareness and training
• Disciplinary process
• Responsibilities after termination or change of employment
• Remote working
• Event reporting

Physical Controls

• Physical security perimeters
• Entry controls
• Securing offices and facilities
• Monitoring physical security
• Protection against physical and environmental threats
• Working in secure areas
• Clear desk and clear screen
• Equipment protection
• Secure disposal and reuse of equipment

Technological Controls

• User endpoint devices
• Privileged access rights
• Information access restriction
• Secure authentication
• Capacity management
• Malware protection
• Vulnerability management
• Configuration management
• Data deletion
• Data masking
• Data leakage prevention
• Backup
• Logging and monitoring
• Clock synchronization
• Network security
• Cryptography
• Secure development lifecycle
• Application security requirements
• Secure coding
• Development and test environments
• Change management
• Test information
• Audit testing and assurance

Practical Exercise

• Review a sample Statement of Applicability
• Match risks to applicable controls
• Identify missing control implementation evidence
• Prepare audit questions for selected Annex A controls
06 Module 4: Audit Principles and Auditor Competence

Topics Covered

• Purpose and objectives of an ISMS audit
• Audit principles
• Integrity
• Fair presentation
• Due professional care
• Confidentiality
• Independence
• Evidence-based approach
• Risk-based approach
• Auditor responsibilities
• Lead Auditor responsibilities
• Audit-team competence
• Auditor behavior and communication
• Maintaining objectivity
• Managing conflicts of interest
• Sampling and professional judgment
• Audit trails and working papers

Auditor Competencies

• Technical knowledge
• Audit knowledge
• Interviewing skills
• Observation skills
• Analytical skills
• Report-writing skills
• Conflict management
• Time management
• Decision-making
• Leadership and team coordination

Practical Exercise

• Auditor role-play
• Interviewing process owners
• Evaluating audit evidence
• Handling disagreement during an audit
07 Module 5: Audit Programme and Audit Initiation

Topics Covered

• Establishing an audit programme
• Audit programme objectives
• Audit scope and criteria
• Audit frequency
• Audit methods
• Audit resources
• Audit risks and opportunities
• Audit-team selection
• Auditor independence
• Audit-team responsibilities
• Contacting the auditee
• Confirming audit feasibility
• Preparing the audit terms of reference
• Confidentiality and security arrangements
• Audit timetable and logistics

Audit Types

• First-party audit
• Internal audit
• Second-party audit
• Supplier audit
• Third-party certification audit
• Surveillance audit
• Recertification audit
• Follow-up audit
• Remote audit
• Hybrid audit

Practical Exercise

• Create an annual ISMS audit programme
• Prepare an audit initiation checklist
• Select an audit team based on competence and independence
08 Module 6: Audit Preparation and Planning

Topics Covered

• Defining audit objectives
• Establishing audit scope
• Establishing audit criteria
• Understanding the auditee’s organization
• Reviewing ISMS documentation
• Reviewing the ISMS scope
• Reviewing the risk assessment methodology
• Reviewing the risk treatment plan
• Reviewing the Statement of Applicability
• Reviewing previous audit reports
• Identifying significant risks
• Preparing an audit plan
• Preparing an audit timetable
• Preparing audit checklists
• Preparing interview questions
• Determining audit sampling
• Planning remote-audit activities
• Allocating responsibilities to audit-team members

Audit Documents

• Audit programme
• Audit plan
• Audit checklist
• Audit notification
• Document-review checklist
• Audit evidence record
• Nonconformity report
• Audit report
• Corrective-action follow-up record

Practical Exercise

• Prepare a complete ISO 27001 audit plan
• Develop a clause-based audit checklist
• Prepare interview questions for IT, HR, facilities, and management
09 Module 7: Conducting the ISMS Audit

Opening Meeting

• Introduction of the audit team
• Confirmation of objectives, scope, and criteria
• Confirmation of audit methods
• Communication channels
• Safety, security, and confidentiality requirements
• Audit timetable
• Availability of guides and escorts
• Handling changes to the audit plan

Audit Evidence Collection

• Interviews
• Observation
• Document review
• Record review
• Technical verification
• Sampling
• Cross-checking evidence
• Reviewing system-generated logs
• Testing control implementation
• Tracing evidence from policy to practice
• Confirming objective evidence

Auditing Techniques

• Open-ended questions
• Closed questions
• Clarifying questions
• Follow-up questions
• Process-based auditing
• Risk-based auditing
• Sampling techniques
• Evidence triangulation
• Remote interviewing
• Auditing outsourced and cloud services

Areas for Audit Verification

• ISMS scope
• Information security policy
• Risk assessment
• Risk treatment
• Statement of Applicability
• Access management
• Incident management
• Backup and recovery
• Supplier security
• Security awareness
• Vulnerability management
• Logging and monitoring
• Business continuity
• Internal audit
• Management review
• Corrective actions

Practical Exercise

• Conduct a simulated opening meeting
• Interview process owners
• Collect and classify audit evidence
• Prepare audit notes and working papers
10 Module 8: Audit Findings and Nonconformity Management

Topics Covered

• Conformity and nonconformity
• Major nonconformity
• Minor nonconformity
• Observation
• Opportunity for improvement
• Positive findings
• Audit evidence supporting a finding
• Statement of requirement
• Statement of objective evidence
• Statement of the nonconformity
• Risk and impact of nonconformity
• Avoiding vague findings
• Avoiding unsupported conclusions
• Root-cause analysis
• Corrective-action requirements
• Corrective-action verification

Common ISO 27001 Audit Findings

• ISMS scope does not reflect actual business operations
• Risk assessment methodology is not consistently applied
• Risk owners are not clearly assigned
• Statement of Applicability lacks justification
• Access reviews are not performed as planned
• Security awareness records are incomplete
• Supplier security reviews are not documented
• Backup restoration tests are not performed
• Vulnerability remediation is overdue
• Internal audit programme is incomplete
• Management review records lack required inputs
• Corrective actions are not verified for effectiveness

Practical Exercise

• Write major and minor nonconformity reports
• Distinguish observation from nonconformity
• Review sample corrective-action plans
• Verify corrective-action effectiveness
11 Module 9: Audit Reporting and Closing the Audit

Topics Covered

• Preparing audit conclusions
• Audit-report structure
• Executive summary
• Audit objectives, scope, and criteria
• Audit-team details
• Audit dates and locations
• Summary of audit activities
• Positive findings
• Nonconformities
• Opportunities for improvement
• Audit conclusions
• Unresolved issues
• Restrictions and limitations
• Distribution and confidentiality
• Conducting the closing meeting
• Presenting findings professionally
• Handling disagreements
• Obtaining acknowledgement of findings
• Issuing the final audit report

Practical Exercise

• Prepare a complete ISMS audit report
• Conduct a closing meeting
• Present findings to senior management
• Respond to auditee questions
12 Module 10: Audit Follow-Up and Certification Process

Topics Covered

• Corrective-action review
• Corrective-action acceptance
• Root-cause evaluation
• Action-plan review
• Evidence review
• Effectiveness verification
• Follow-up audit
• Closure of nonconformities
• Escalation of overdue actions
• Audit-programme improvement
• Certification audit stages
• Stage 1 audit
• Stage 2 audit
• Surveillance audits
• Recertification audits
• Certification decision process
• Auditor competence and continual development

Practical Exercise

• Review a corrective-action plan
• Verify evidence submitted by an auditee
• Prepare a follow-up audit report
• Conduct a certification-readiness review
13 Hands-On Labs and Workshops
1. ISMS Scope Definition Workshop
2. Information Asset Identification Lab
3. Information Security Risk Assessment Lab
4. Risk Treatment Plan Preparation Lab
5. Statement of Applicability Review Lab
6. ISO/IEC 27001 Clause Interpretation Workshop
7. Annex A Control Mapping Lab
8. ISMS Document Review Exercise
9. Audit Programme Preparation Lab
10. Audit Plan Development Lab
11. Audit Checklist Preparation Lab
12. Auditor Interview Skills Workshop
13. Evidence Collection and Sampling Lab
14. Access Control Audit Simulation
15. Incident Management Audit Simulation
16. Supplier Security Audit Simulation
17. Backup and Business Continuity Audit Simulation
18. Nonconformity Writing Workshop
19. Corrective-Action Verification Lab
20. Complete ISMS Audit Simulation
14 Assignments
• Prepare an ISMS scope statement
• Create an information asset register
• Develop a basic risk assessment
• Prepare a risk treatment plan
• Review a Statement of Applicability
• Map ISO/IEC 27001 clauses to audit evidence
• Prepare an Annex A control checklist
• Develop an annual audit programme
• Prepare a five-day audit plan
• Create an audit interview questionnaire
• Evaluate sample audit evidence
• Write three audit findings
• Prepare a corrective-action request
• Review a sample audit report
• Develop an audit follow-up plan
15 Mini Projects

Mini Project 1: ISMS Readiness Assessment

Assess a sample organization against ISO/IEC 27001:2022 requirements and prepare a readiness-gap report.

Mini Project 2: Supplier Security Audit

Audit a cloud or IT service provider using supplier security requirements and documented evidence.

Mini Project 3: Internal ISMS Audit

Plan and conduct an internal audit covering risk management, access control, incident management, and documented information.

Mini Project 4: Annex A Control Effectiveness Review

Evaluate selected Annex A controls and identify implementation gaps.
16 Capstone Project

Enterprise ISO/IEC 27001:2022 Certification Readiness Audit

Participants will perform a complete simulated audit for an organization preparing for ISO/IEC 27001 certification.

Capstone Activities

1. Understand the organization and business context
2. Define audit objectives, scope, and criteria
3. Review ISMS documentation
4. Examine the risk assessment process
5. Review the Statement of Applicability
6. Prepare an audit programme and audit plan
7. Conduct opening meeting
8. Interview process owners
9. Collect objective evidence
10. Audit selected Annex A controls
11. Identify and classify findings
12. Prepare nonconformity reports
13. Conduct closing meeting
14. Prepare the final audit report
15. Review corrective-action plans
16. Conduct follow-up verification
17. Present audit conclusions to management

Capstone Deliverables

• Audit programme
• Audit plan
• Audit checklist
• Evidence collection records
• Audit working papers
• Nonconformity reports
• Corrective-action review
• Final audit report
• Management presentation
17 Real-Time Job-Oriented Scenarios
• Auditing an organization’s ISMS scope after a business expansion
• Reviewing access-control evidence for privileged users
• Auditing employee onboarding and offboarding
• Verifying periodic access reviews
• Reviewing backup policies and restoration-test records
• Auditing cloud-service provider security controls
• Checking vulnerability-management records
• Reviewing security incident response evidence
• Auditing security awareness and training records
• Verifying supplier risk assessments
• Reviewing business continuity and disaster recovery tests
• Auditing encryption and key-management processes
• Checking logging and monitoring controls
• Reviewing internal audit and management review records
• Evaluating corrective actions from a previous audit
• Preparing an organization for Stage 1 certification audit
• Supporting a Stage 2 certification audit
• Conducting a surveillance-audit follow-up
18 Troubleshooting and Audit Challenges
• Auditee provides incomplete evidence
• Documents do not match actual practices
• Risk assessment does not cover critical assets
• Statement of Applicability lacks adequate justification
• Control ownership is unclear
• Process owner disagrees with an audit finding
• Audit evidence is insufficient to support a conclusion
• Different departments provide conflicting information
• Audit scope is too broad for the available time
• Remote audit access is unavailable
• Logs are missing or overwritten
• Corrective actions address symptoms rather than root causes
• Nonconformities are not closed within the agreed timeframe
• Auditor independence is challenged
• Confidential information is exposed during evidence collection
19 Industry Tools and Templates

Governance and Compliance Tools

• ServiceNow GRC
• RSA Archer
• MetricStream
• OneTrust
• AuditBoard
• IBM OpenPages
• Microsoft Purview Compliance Manager

Security and Monitoring Tools

• Microsoft Sentinel
• Splunk
• IBM QRadar
• Elastic Security
• Microsoft Defender
• Nessus
• Qualys
• Tenable
• CrowdStrike

Documentation and Collaboration Tools

• Microsoft Word
• Microsoft Excel
• Microsoft SharePoint
• Microsoft Teams
• Confluence
• Jira
• Google Workspace

Audit Templates

• ISMS scope template
• Risk register
• Risk treatment plan
• Statement of Applicability
• Audit programme
• Audit plan
• Audit checklist
• Interview questionnaire
• Evidence register
• Nonconformity report
• Corrective-action tracker
• Audit report
• Follow-up audit report
20 Best Practices
• Audit against documented criteria and objective evidence
• Maintain independence and impartiality
• Use a risk-based audit approach
• Avoid assumptions and unsupported conclusions
• Record evidence accurately
• Ask process-focused questions
• Validate findings with the auditee
• Protect confidential information
• Maintain complete audit trails
• Link every finding to a requirement and evidence
• Distinguish nonconformity from observation
• Focus corrective actions on root causes
• Verify corrective-action effectiveness
• Maintain auditor competence
• Use sampling consistently
• Communicate findings clearly and professionally
21 Certification Preparation
The course can include preparation for relevant auditor examinations and certification pathways, depending on the selected certification provider.

Possible certification pathways include:

• CQI/IRCA ISO/IEC 27001:2022 Lead Auditor
• PECB ISO/IEC 27001 Lead Auditor
• Exemplar Global ISO/IEC 27001 Auditor
• NBQP-registered ISMS Lead Auditor training
• ISO/IEC 27001 Internal Auditor certification
Certification eligibility, examination format, experience requirements, and auditorregistration requirements vary by provider. A training certificate alone does not automatically confer certification as an internationally registered lead auditor.
22 Mock Interviews and Assessment

Technical Questions

• Explain the purpose of an ISMS.
• What is the difference between ISO/IEC 27001 and ISO/IEC 27002?
• Explain the purpose of the Statement of Applicability.
• How do you audit risk assessment and risk treatment?
• What is the difference between major and minor nonconformity?
• How do you collect objective audit evidence?
• What are the responsibilities of a Lead Auditor?
• Explain first-party, second-party, and third-party audits.
• How do you verify corrective-action effectiveness?
• What is the role of ISO 19011 in ISMS auditing?

Practical Assessments

• Audit-plan preparation
• Audit-checklist development
• Interview simulation
• Evidence evaluation
• Nonconformity writing
• Closing-meeting presentation
• Audit-report preparation
• Corrective-action verification
• Final written examination

Expected Learning Outcomes

After completing the course, participants should be able to:

• Explain ISO/IEC 27001:2022 requirements
• Understand Annex A control objectives and implementation evidence
• Plan an ISMS audit
• Prepare audit checklists and audit schedules
• Conduct interviews and collect objective evidence
• Evaluate conformity and nonconformity
• Prepare audit findings and reports
• Lead audit meetings
• Review corrective actions
• Conduct audit follow-up activities
• Support internal, supplier, and certification-readiness audits

Tools & Technologies

Every tool listed here is installed, configured and used in a hands-on lab session.

Core Tools

Hands-On Labs

Practical Environment

Industry-Standard Tools

Real-World Setup

Guided Exercises

Skill Building

Sample Datasets

Practice Material

Practice & Projects

Mini Projects

Applied Practice

Assignments

Mentor Reviewed

Doubt Sessions

Live Support

Career Readiness

Resume Building

Career Support

Mock Interviews

Interview Prep

Certification Prep

Global Recognition

Deployment & Delivery

Production Practices

Real-World Ready

Best Practices

Industry Standards

545+
Hands-On Lessons
22
Core Modules
24 hours
Training Duration
100%
Practical Training

You don't just learn ISO/IEC 27001:2022 LEAD AUDITOR. You ship it.

Three major projects, each mirroring how production teams actually work — from guided foundations to a portfolio-ready capstone.

PROJECT // 01

Guided Foundation Project

→Requirement Analysis

→Guided Implementation

→Mentor Review

→Iteration

Foundation Beginner

Apply the fundamentals in a structured, mentor-reviewed project

Take the core concepts from the first half of the curriculum and apply them to a realistic scenario, with guidance and feedback from your mentor at every step.

Structured project brief
Step-by-step implementation
Mentor feedback and review
Documented outcome
Stack Core Concepts Best Practices
PROJECT // 02

Applied Practice Project

→Scenario Design

→Independent Build

→Testing & Validation

→Peer Review

Applied Intermediate

Build a more independent project mirroring real production scenarios

Work through a project that combines multiple concepts from the curriculum, closer to how work is actually structured on the job — less hand-holding, more ownership.

End-to-end implementation
Testing and validation
Documentation
Peer/mentor review
Stack Applied Skills Testing
PROJECT // 03

Capstone Project

→Planning

→End-to-End Build

→Review & Refinement

→Presentation

Capstone Advanced

Take a project from requirements to a polished, portfolio-ready deliverable

Your final project — plan, build, test and present a complete solution using everything covered in the curriculum, reviewed by mentors before you graduate.

Complete working solution
Presentation-ready documentation
Mentor sign-off
Portfolio-ready deliverable
Stack Full Curriculum Portfolio

All 3 projects go directly into your portfolio & resume — reviewed by mentors before you graduate.

See Sample Project Reports

Upcoming Batches

No upcoming batches scheduled right now. Enquire to get notified.

Why Radical Technologies

Live Online Training
  • Highly practical oriented training
  • Installation support on your system
  • 24/7 Email and Phone support
  • 100% Placement Assistance
  • Global Certification Preparation
  • Trainer-Student Interactive Portal
  • Assignments and Projects by Mentors
Live Classroom Training
  • Weekend / Weekdays / Morning / Evening batches
  • 80:20 Practical and Theory ratio
  • Real-life Case Studies
  • Easy make-up for missed sessions
  • PSI | Kryterion | Redhat Test Centers
  • Lifetime Video Classroom Access (coming soon)
  • Resume Prep and Mock Interviews
Self-Paced Training
  • Learn 300+ courses at your own time
  • 50,000+ Satisfied Learners
  • Course Completion Certificate
  • Practical Labs available
  • Mentor Support available
  • Doubt Clearing Session available
  • 10% Discounted Global Certification

Like the Curriculum? Let's Get Started

Join 50,000+ students already enrolled at Radical Technologies

Enroll Now

Global Certification

Radical Technologies is the leading IT certification institute in Kochi, offering globally recognized certifications across various domains. With expert trainers and comprehensive materials, we ensure students gain in-depth knowledge and hands-on experience to excel in their careers. Our certification programs are tailored to meet industry standards — from cloud technologies to data science — empowering individuals to stay ahead in the ever-evolving tech landscape.
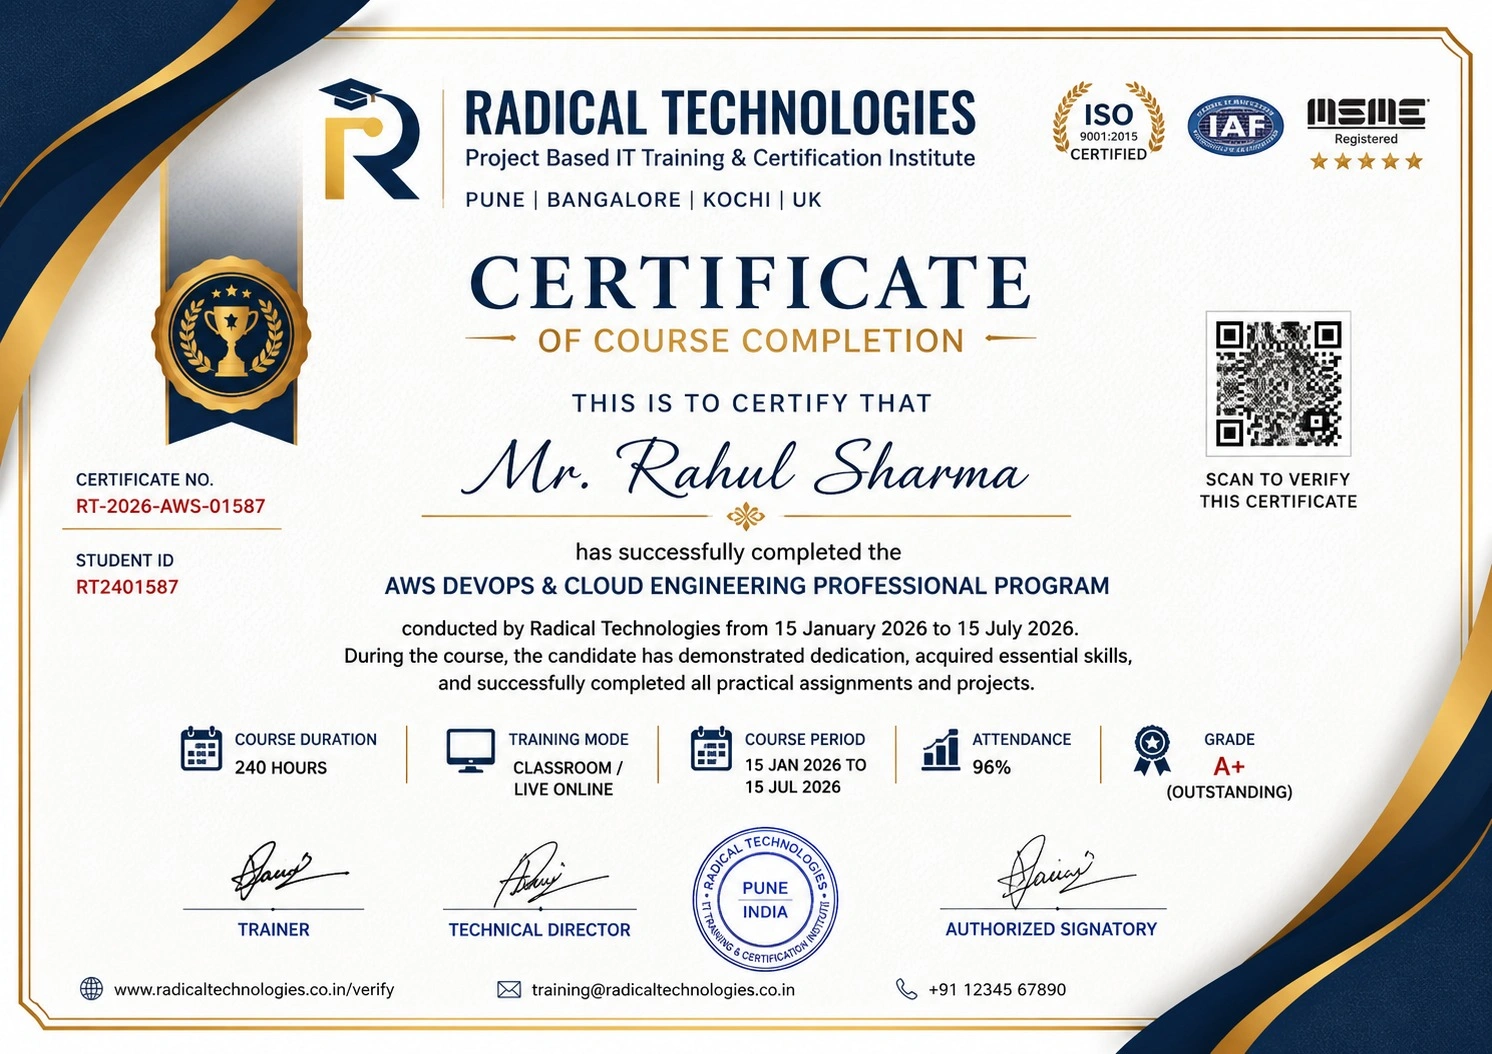
Certificate of Completion

Career Services

At Radical Technologies, we are committed to your success beyond the classroom. Our 100% Job Assistance program ensures that you are not only equipped with industry-relevant skills but also guided through the job placement process. With personalised resume building, interview preparation, and access to our extensive network of hiring partners, we help you take the next step confidently into your IT career.

Career Support

Course Completed? Need next steps?
Need Interview Supports?
Need Job Assistance?
Came from any other Institute?

Join our Brush-up Session & get support until you find a job!

Get Started

Radical Learning Eco-System

Exam Simulator

Cloud SandBox

Hands-on Cloud Lab

Developer Coding Ground

Student Reviews

4.7★
Average learner rating
50K+
Students trained
30+
Hiring companies alumni work at
100%
Placement assistance
4.7
★★★★★

Course Rating

★★★★★
79%
★★★★☆
16%
★★★☆☆
3%
★★☆☆☆
1%
★☆☆☆☆
1%

Our Alumni Work At
Accenture
Amazon
Avisys Services
Birlasoft
Capgemini
Catchpoint
Cognizant
Darwish Cybertech
DataVision
GiBots
Google
Groots Software
HCL Technologies
IBM
Info Gain
Infosys
ITCube Solutions
KPIT
L&T Infotech
Microsoft
Mphasis
mPhatek
Oracle
Quantbit Technologies
Saina Cloud
TCS
Tech Mahindra
Wipro
YASH Technologies
Zensar Technologies
Accenture
Amazon
Avisys Services
Birlasoft
Capgemini
Catchpoint
Cognizant
Darwish Cybertech
DataVision
GiBots
Google
Groots Software
HCL Technologies
IBM
Info Gain
Infosys
ITCube Solutions
KPIT
L&T Infotech
Microsoft
Mphasis
mPhatek
Oracle
Quantbit Technologies
Saina Cloud
TCS
Tech Mahindra
Wipro
YASH Technologies
Zensar Technologies

ISO/IEC 27001:2022 Lead Auditor Course Certification with Training In Kochi

Get a Call Back from Our Career Assistance Team

Request Callback